Quantum-Safe Key Management in Cloud Environments
Compare cloud KMS, HSM and control layers to plan post‑quantum key migration for long‑life data and regulated workloads.
Read more
Compare cloud KMS, HSM and control layers to plan post‑quantum key migration for long‑life data and regulated workloads.
Read more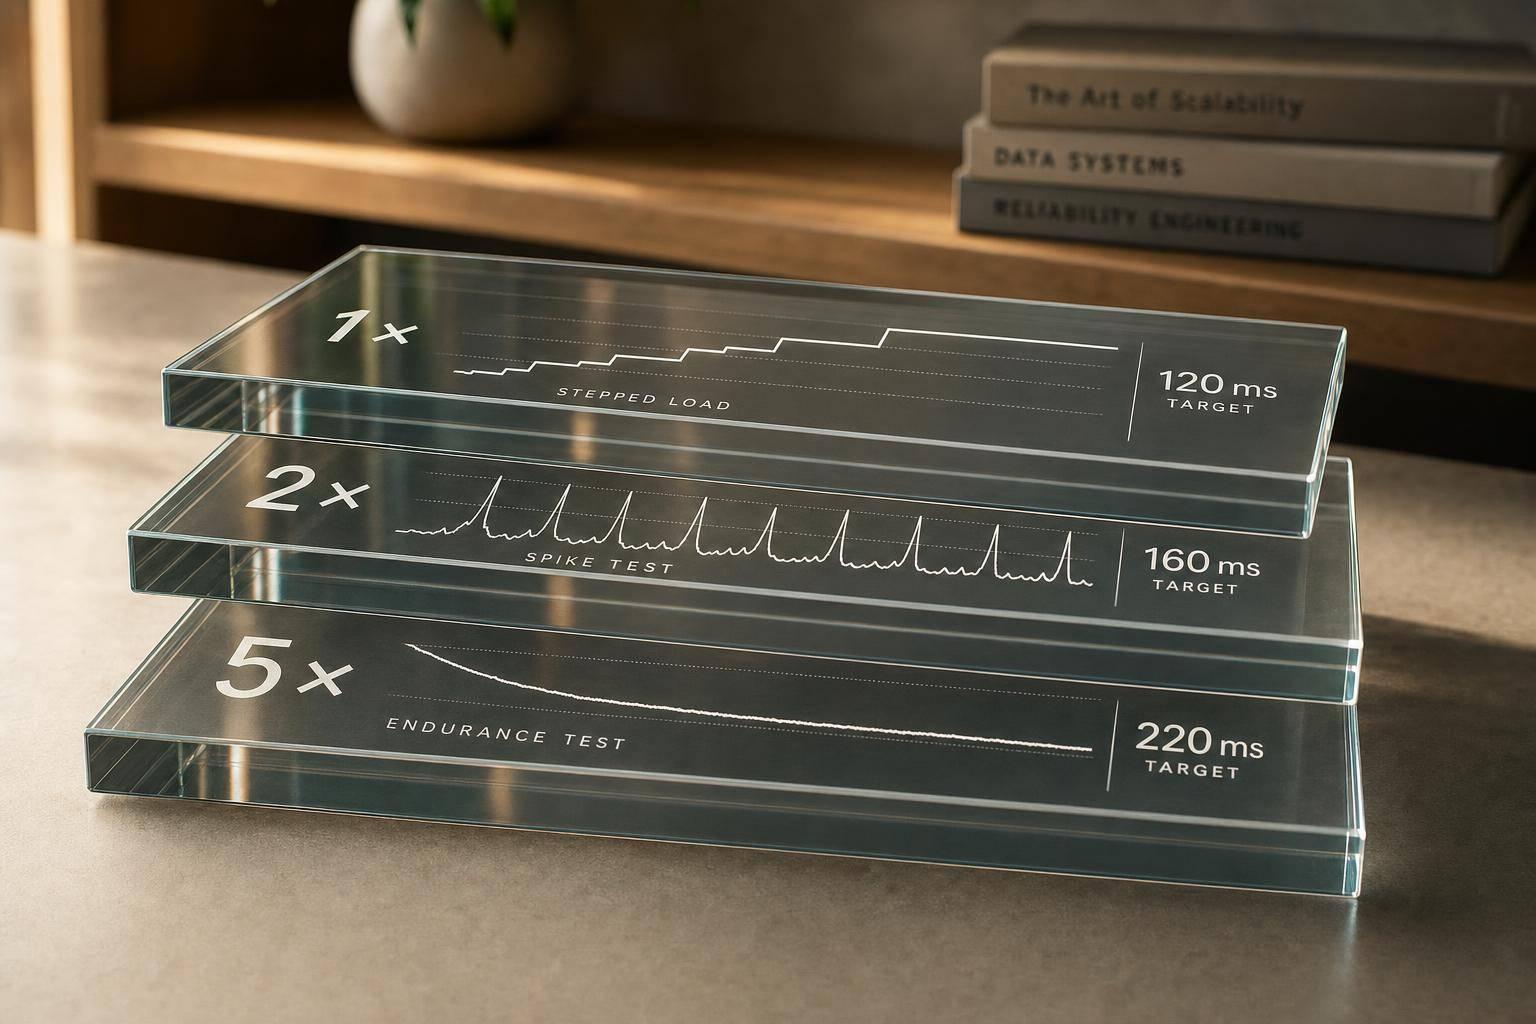
Test databases at 1×, 2× and 5× scale: set numeric SLAs, mirror production, run stepped/burst/endurance tests and fix bottlenecks.
Read more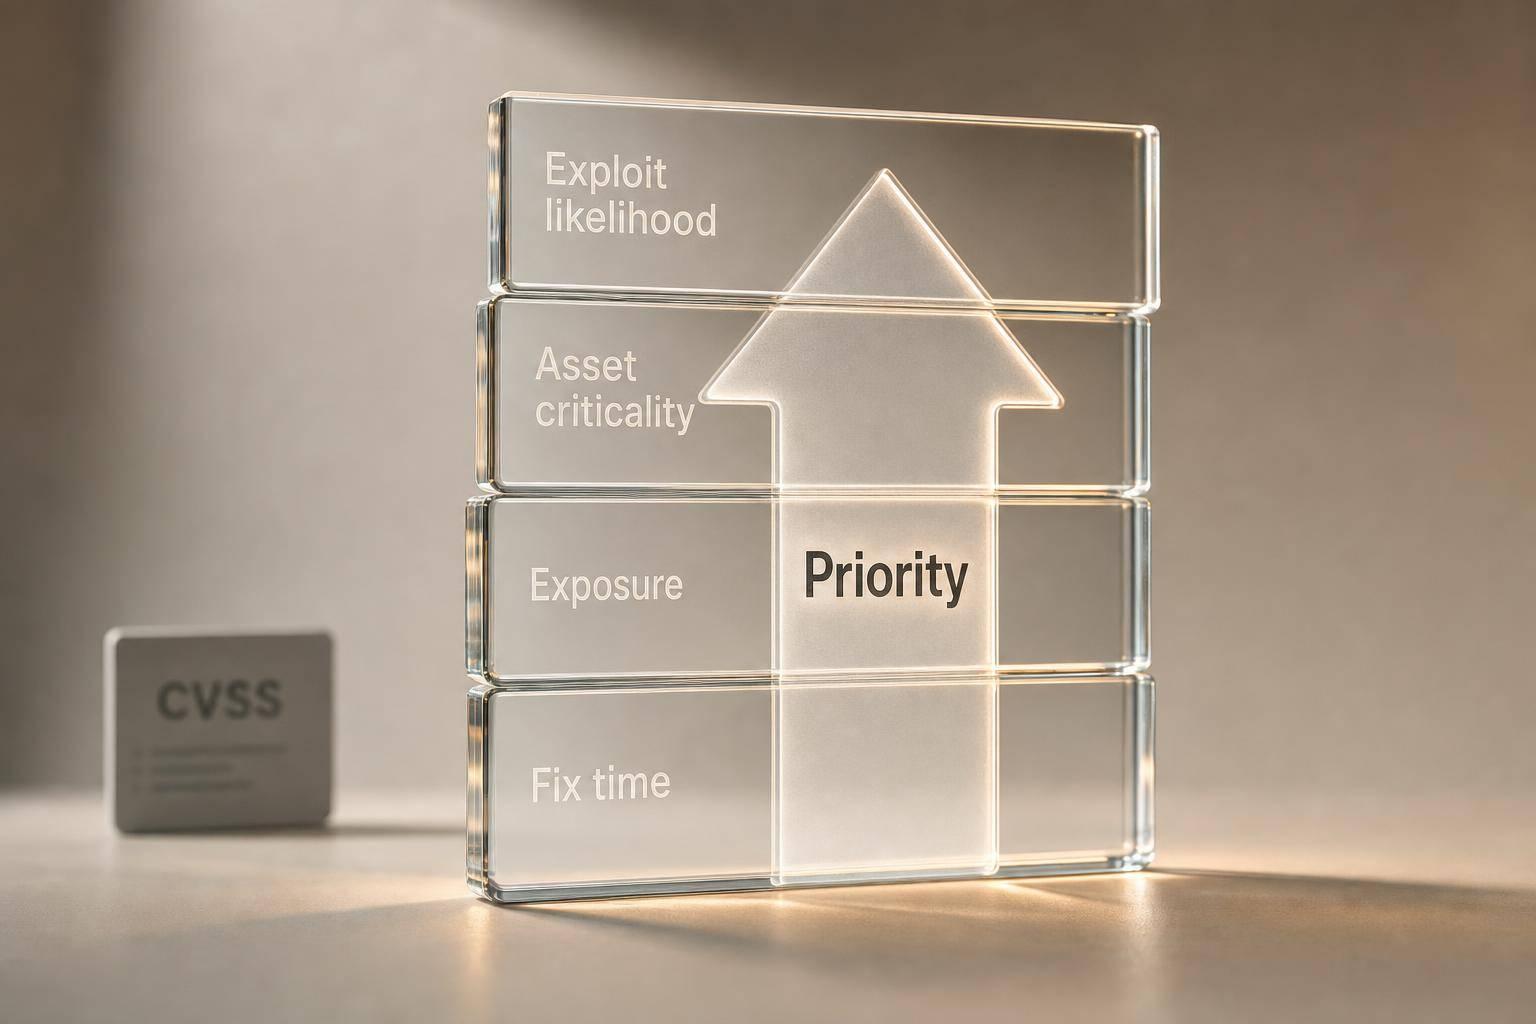
Prioritise fixes by exploit likelihood, asset criticality, exposure and fix time — not CVSS alone.
Read more
Small latency gaps hide bigger trade-offs; region choice, storage tier and autoscaling usually decide which cloud is best for UK apps.
Read more
AI cuts false alerts and speeds remediation across AWS, Azure and GCP—if controls stay explainable and high‑risk cases keep human review.
Read more
Practical guide to safe Kubernetes rolling deployments: set probes, handle SIGTERM, tune maxSurge/maxUnavailable, monitor and rollback.
Read more
Six core metrics—latency, traffic, UX, uptime, capacity and cost—with thresholds and standard labels for consistent multi‑cloud monitoring.
Read more
Practical guidance on structuring Terraform for multi-cloud: split state, simple modules, secure identities and cost controls.
Read more
Practical steps to reduce video CDN bills: optimise cache keys and TTLs, add origin shielding, tune encoding/ABR, use multi‑CDN routing and monitor £/GB.
Read more
Treat every CI/CD version bump as a risk: check compatibility, test in staging, rehearse rollback, and verify post-release.
Read more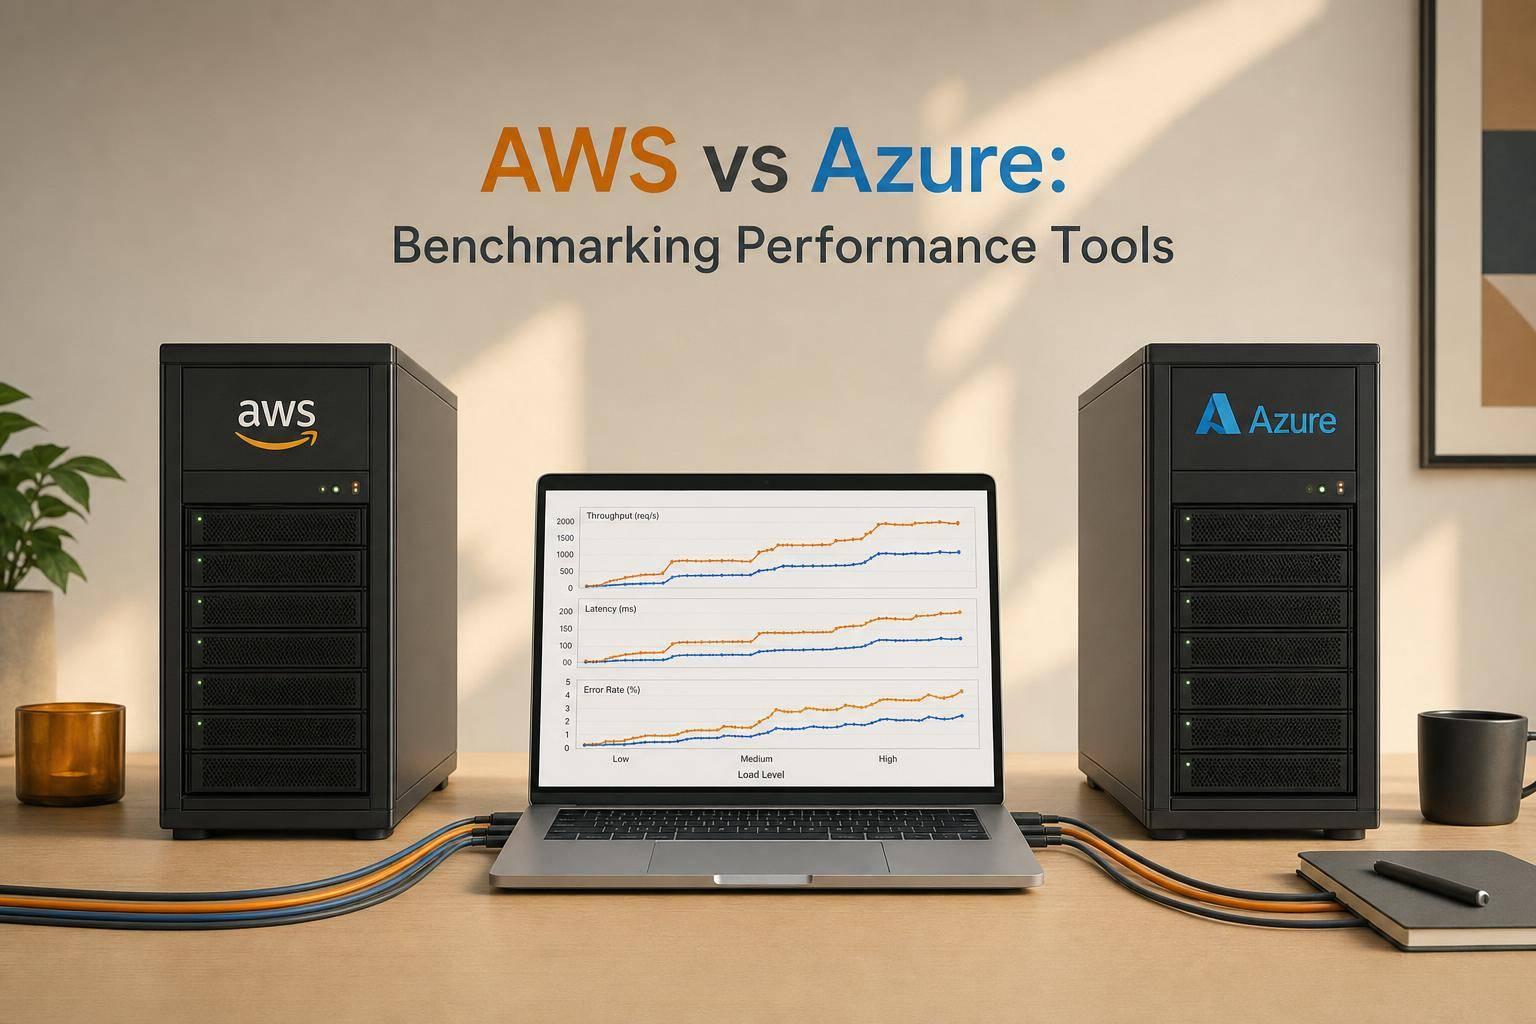
Managed testing is faster to start, but deeper control needs more setup — benchmark at multiple load levels with the same external tool.
Read more
Map identity sources, match each app to SAML/OIDC/OAuth, centralise policies, phase rollouts and test failover for resilient hybrid SSO.
Read more