Multi-Cloud Compliance: Role of Policy Versioning
Track, test and enforce versioned policy-as-code across AWS, Azure and GCP to simplify audits, prevent drift and reduce compliance risk.
Read moreBlog posts in the Automation category
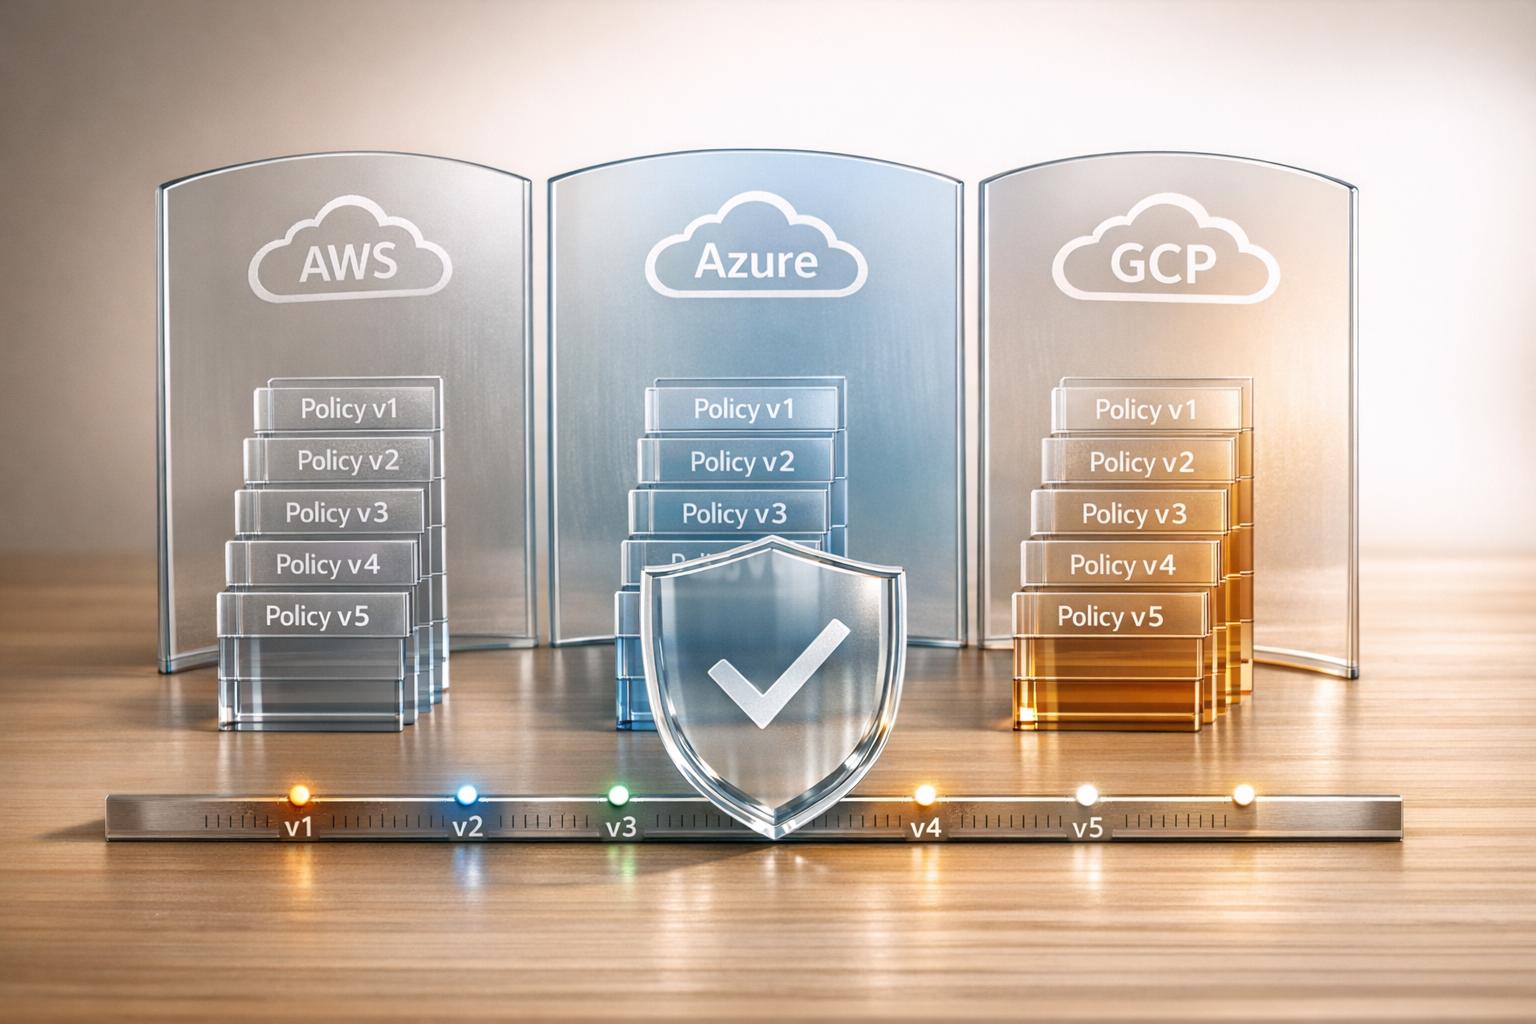
Track, test and enforce versioned policy-as-code across AWS, Azure and GCP to simplify audits, prevent drift and reduce compliance risk.
Read more
Practical five-step guide to plan, create, automate and test GCP snapshots for reliable, cost‑aware disaster recovery.
Read more
Run fast, isolated unit tests early in CI/CD, use JUnit XML reports, parallelise suites and monitor flaky tests for reliable pipelines.
Read more
Centralised CI/CD with distributed runners, IaC and container workflows for secure, consistent hybrid cloud delivery.
Read more
Manage service mesh configs using version control, preflight validation, staged rollouts, observability and fast rollback to avoid outages.
Read more
Automated CI/CD pipelines speed delivery but risk access misconfigurations, leaked secrets, vulnerable dependencies and artefact tampering.
Read more
Hybrid cloud failover keeps services running by automating detection, replication and recovery across on‑prem and cloud environments.
Read more
Automated compliance enforces policies, prevents misconfigurations and idle resources, and cuts cloud spend by up to 35%.
Read more
Self-healing systems detect, diagnose and remediate microservice failures to cut downtime, costs and on-call fatigue.
Read more
Troubleshoot CI/CD build failures with logs, local reproduction, linters and debug traces to reduce downtime and prevent repeats.
Read more
GitOps enforces declarative, auditable, self-healing Kubernetes deployments unlike fragile push-based CI/CD.
Read more
Consistent, automated cloud tagging gives CTOs clear cost allocation, reduces waste and enforces accountability.
Read more